
2026 iAwards QLD Finalist
Artificial Intelligence Technology, an AIIA program
You have already done
more of it than you think.
You hold SOC 2. A customer now wants ISO 27001. Most of that work is sitting in evidence you already collected, and the expensive part is finding out which parts. We answer that from a control graph of 868 frameworks, where 68,166 mappings survived a pass that argued against them and 42,088 did not, and you can read the ones that did not.
For those 598 pairs the answer is already written, so asking it takes a moment rather than a project. Any other pair is built to order at the same price, and that one takes as long as the work takes.
Not sure where to start? Find the right framework →
The Knowledge Graph
868 Frameworks. 315K+ Connections.
Every node is a compliance framework. Every line is a real control-to-control mapping. Hover to explore — this is the engine behind the platform.
Loading 868 frameworks...
Sign up to search, explore, and map controls across the entire graph.
Explore the Full GraphYour agent can ask.
Ours answers.
Point any MCP client at one URL and an agent can ask how much of one standard a company already satisfies by holding another, get a percentage back with the reasoning behind every claim, and buy the report. No account, no sales call, no human in the loop.
https://api.theartofservice.com/mcp- 01agent_coverage_crosswalk returns what a company already satisfies and what is a genuine gap.
- 02agent_crosswalk_provenance returns the reasoning, the source document and the date behind each claim.
- 03The agent hands back a checkout URL, and the full report is emailed on payment.
The Problem
You're Doing Compliance the Hard Way
Every compliance team hits the same walls. Here's what's costing you time and money right now.
Weeks Wasted on Spreadsheets
Your team manually maps controls between frameworks in Excel. It takes weeks. By the time you finish, the frameworks have updated and your mappings are already stale.
Paying Premium Rates for Manual Lookups
Traditional compliance consulting spends hours doing what a knowledge graph does in milliseconds — looking up which controls in Framework A correspond to Framework B.
Gaps You Don't Know About
You think you're covered because you passed one audit. But without cross-framework mapping, you have no idea which controls are missing for your next certification.
What You Get
The compliance intelligence a consultant provides
— at a fraction of the cost.
Eleven capabilities you cannot get from spreadsheets, PDFs, or generic AI chatbots.
Cross-Framework Mapping
See ISO 27001 to SOC 2 mappings with the reasoning behind each one
315K+ pre-built control-to-control mappings. Pick any two frameworks — instantly see which controls overlap, which are unique, and where your gaps are.
AI That Knows Compliance
Ask anything. Get answers grounded in real data.
Not ChatGPT guessing — an AI advisor backed by 868 frameworks and 42,974+ controls in a knowledge graph. Every answer is traceable to source controls.
- CC7.2 — Change management monitoring
- CC8.1 — Logical access controls
- A1.2 — Recovery time objectives
Agentic Compliance Workflows
Set a goal. The AI executes it autonomously.
Define a compliance task — gap analysis, remediation plan, coverage report — and the AI agent executes it step by step. Real-time tool calls against the knowledge graph, streamed to your screen as structured reports.
Policy Document Mapping
Upload your PDF. See how it maps to any framework.
Upload a security policy PDF and the AI agent extracts its contents, searches for relevant sections, and maps them control-by-control against your target framework. Get a coverage report with covered, partial, and gap status for every control.
Maturity Diagnostics
Know exactly where you stand. Not a vague "you need work."
824+ targeted assessments with radar charts, domain-level scoring, gap analysis, and concrete learning paths to close weaknesses.
Framework Galaxy
See how all 868 frameworks connect visually.
Interactive force-directed graph showing every framework, their shared controls, and clustering. Click any node to drill into details.
Search Everything
Find any control, question, or framework instantly.
Full-text search across 1M+ questions, 42,974+ controls, and 868 frameworks. Filter by type. Click through to full context.
AC-2Account Management
NIST 800-53
A.9.2.1User Registration & De-registration
ISO 27001
SOC 2 Type II
Trust Services Criteria
Document Gap Analysis & Rewrite
Upload a policy, check it against real controls, rewrite it to 100%.
Upload any policy document and have it checked against 42,974+ real controls from our knowledge graph. Then use the Gap-Closing Draft, which rewrites your document with language written against each gap found, grounded in actual framework controls. It is a draft for review, not a compliant document.
Compliance Portfolio
Your compliance journey in one place.
Track managed frameworks, save comparisons, create remediation tasks, and add notes to individual controls. Everything you need to stay on top of your compliance posture.
API Access
Full programmatic access to all endpoints.
Generate API keys to integrate compliance data into CI/CD pipelines, dashboards, and reporting tools. Automate your compliance workflows with a RESTful API.
CI/CD Pipeline
taos_live_7f3a...
Dashboard Widget
taos_live_9b1c...
curl -H "Authorization: Bearer taos_live_..." \
  https://api.theartofservice.com/api/frameworks/
Team Collaboration
Track compliance maturity together.
Create an organization, invite your team, and collaborate on compliance. Shared assessments and a team dashboard show your collective posture at a glance.
Try It Now
See Real Mappings. No Sign-Up.
Pick any two frameworks and see how their controls map to each other — live, using real data.
Built on Real Data
Not Another Chatbot Wrapper.
A Compliance Knowledge Graph.
Every answer, mapping, and gap report is computed from a 2.2 million-node graph database — not LLM hallucinations. This is the data infrastructure your compliance team has been building in spreadsheets.
What the platform has done so far
Read from the graph on every render. The rejected mappings are queryable without an account.
Where the graph came from
Professionals at more than 900 organisations have bought The Art of Service material since 2000, from Fortune 500 manufacturers and global technology firms to public sector agencies.
The knowledge graph is what over 25 years of that work turned into. The buyers are named, and every one traces to a paid order.
Graph Nodes
Neo4j knowledge graph with frameworks, controls, domains, questions, and assessments
Jurisdictions
Frameworks from US, EU, UK, Australia, Canada, Japan, Singapore, and more
Crosswalk Pairs Signed Off
Framework pairs reviewed end to end and released, each stating its own level of review
Control Mappings
Real control-to-control relationships, not keyword matching or AI guesses
Assessments
Targeted compliance diagnostics with 1M+ questions across every domain
Controls Indexed
Every control from ISO, NIST, SOC, PCI, HIPAA, GDPR, and 862 more frameworks
Frameworks included
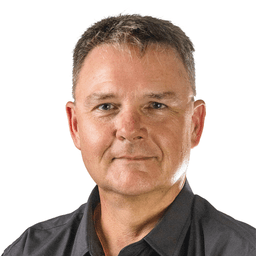
Who built this
Gerard Blokdyk
I have spent 25 years writing about compliance frameworks for practitioners, and the same problem kept coming back: every standard gets published as a flat list, so the work you already did for one counts for nothing when the next customer asks for another.
So this is a graph rather than a checklist. 868 frameworks, 42,974 controls, and the relationships between them judged one at a time rather than scored for similarity. 68,166 of those judgements survived a pass that argued against them. 42,088 did not, and I kept those too, because a mapping nobody could have disagreed with is not a judgement.
If a claim on this site is wrong, it is wrong under my name. Tell me and I will fix it: support@theartofservice.com.
How It Works
From Assessment to Action
A streamlined workflow that saves weeks of manual effort — with real product UI, not abstract diagrams.
Assess Your Maturity
Run targeted compliance diagnostics across any of 824+ assessments. Rate your maturity on a 1-5 scale and get instant radar-chart results with gap analysis.
Information security policies are documented and approved
Access control procedures are reviewed quarterly
Incident response plan has been tested in last 12 months
Map Controls Across Frameworks
See exactly how controls map between frameworks. Identify coverage, gaps, and overlaps between your current certifications and target frameworks.
Get AI-Powered Guidance
Ask the AI advisor anything, or run agentic workflows — gap analysis, remediation plans, coverage reports — that autonomously query 868 frameworks and 315K+ control mappings.
SI-4 (System Monitoring) requires continuous monitoring capabilities. Based on your ISO 27001 assessment:
- Extend A.12.4 (Logging) to include real-time alerting
- Add automated log analysis per NIST guidelines
- Document monitoring procedures in your ISMS
Sources: NIST SP 800-53 SI-4, ISO 27001 A.12.4.1
Upload & Map Your Policies
Upload a security policy PDF and the AI agent extracts its contents, maps them control-by-control against your target framework, and produces a coverage report showing what's covered, partial, and missing.
Manage & Collaborate
Build your compliance portfolio with tracked frameworks, saved comparisons, and remediation tasks. Invite your team, share assessments, and monitor collective maturity from a team dashboard.
Not Sure Which Framework You Need?
Answer 5 quick questions about your industry, location, and data types. We'll recommend the right frameworks from 868+ standards.
What industry does your organisation operate in?
Select your primary industry
Pricing
Simple, Transparent Pricing
Cross-framework compliance mapping at a fraction of consulting costs.
Free
Full platform access — no credit card required
- 824+ compliance assessments
- Radar charts, gap analysis & learning paths
- 868 framework browser
- Cross-framework mapping (315K+)
- Knowledge graph explorer
- 3 AI advisory queries per day
- 3 search queries per day
Professional
7-day free trial — no charge until day 8
- Everything in Free, plus:
- Unlimited AI Compliance Advisory
- Agentic workflows (gap analysis, remediation, coverage)
- Upload documents, checked against 42,974+ knowledge graph controls
- Gap-Closing Draft: AI drafts language against the gaps found
- Structured compliance reports with export
- Unlimited full-text search
- Framework self-assessment (control-by-control)
- PDF & Excel report exports
- CSV data exports
- Compliance portfolio & saved comparisons
- API keys for programmatic access
- Team & organization management
- Priority support
Stop Paying Consultants
to Read Spreadsheets.
868 frameworks. 315K+ mappings. AI agents that execute compliance tasks.
Upload your policies, check them against 42,974+ real controls, and get a Gap-Closing Draft. Start free.